
Amazon links open-source software library hacks to North Korean hackers

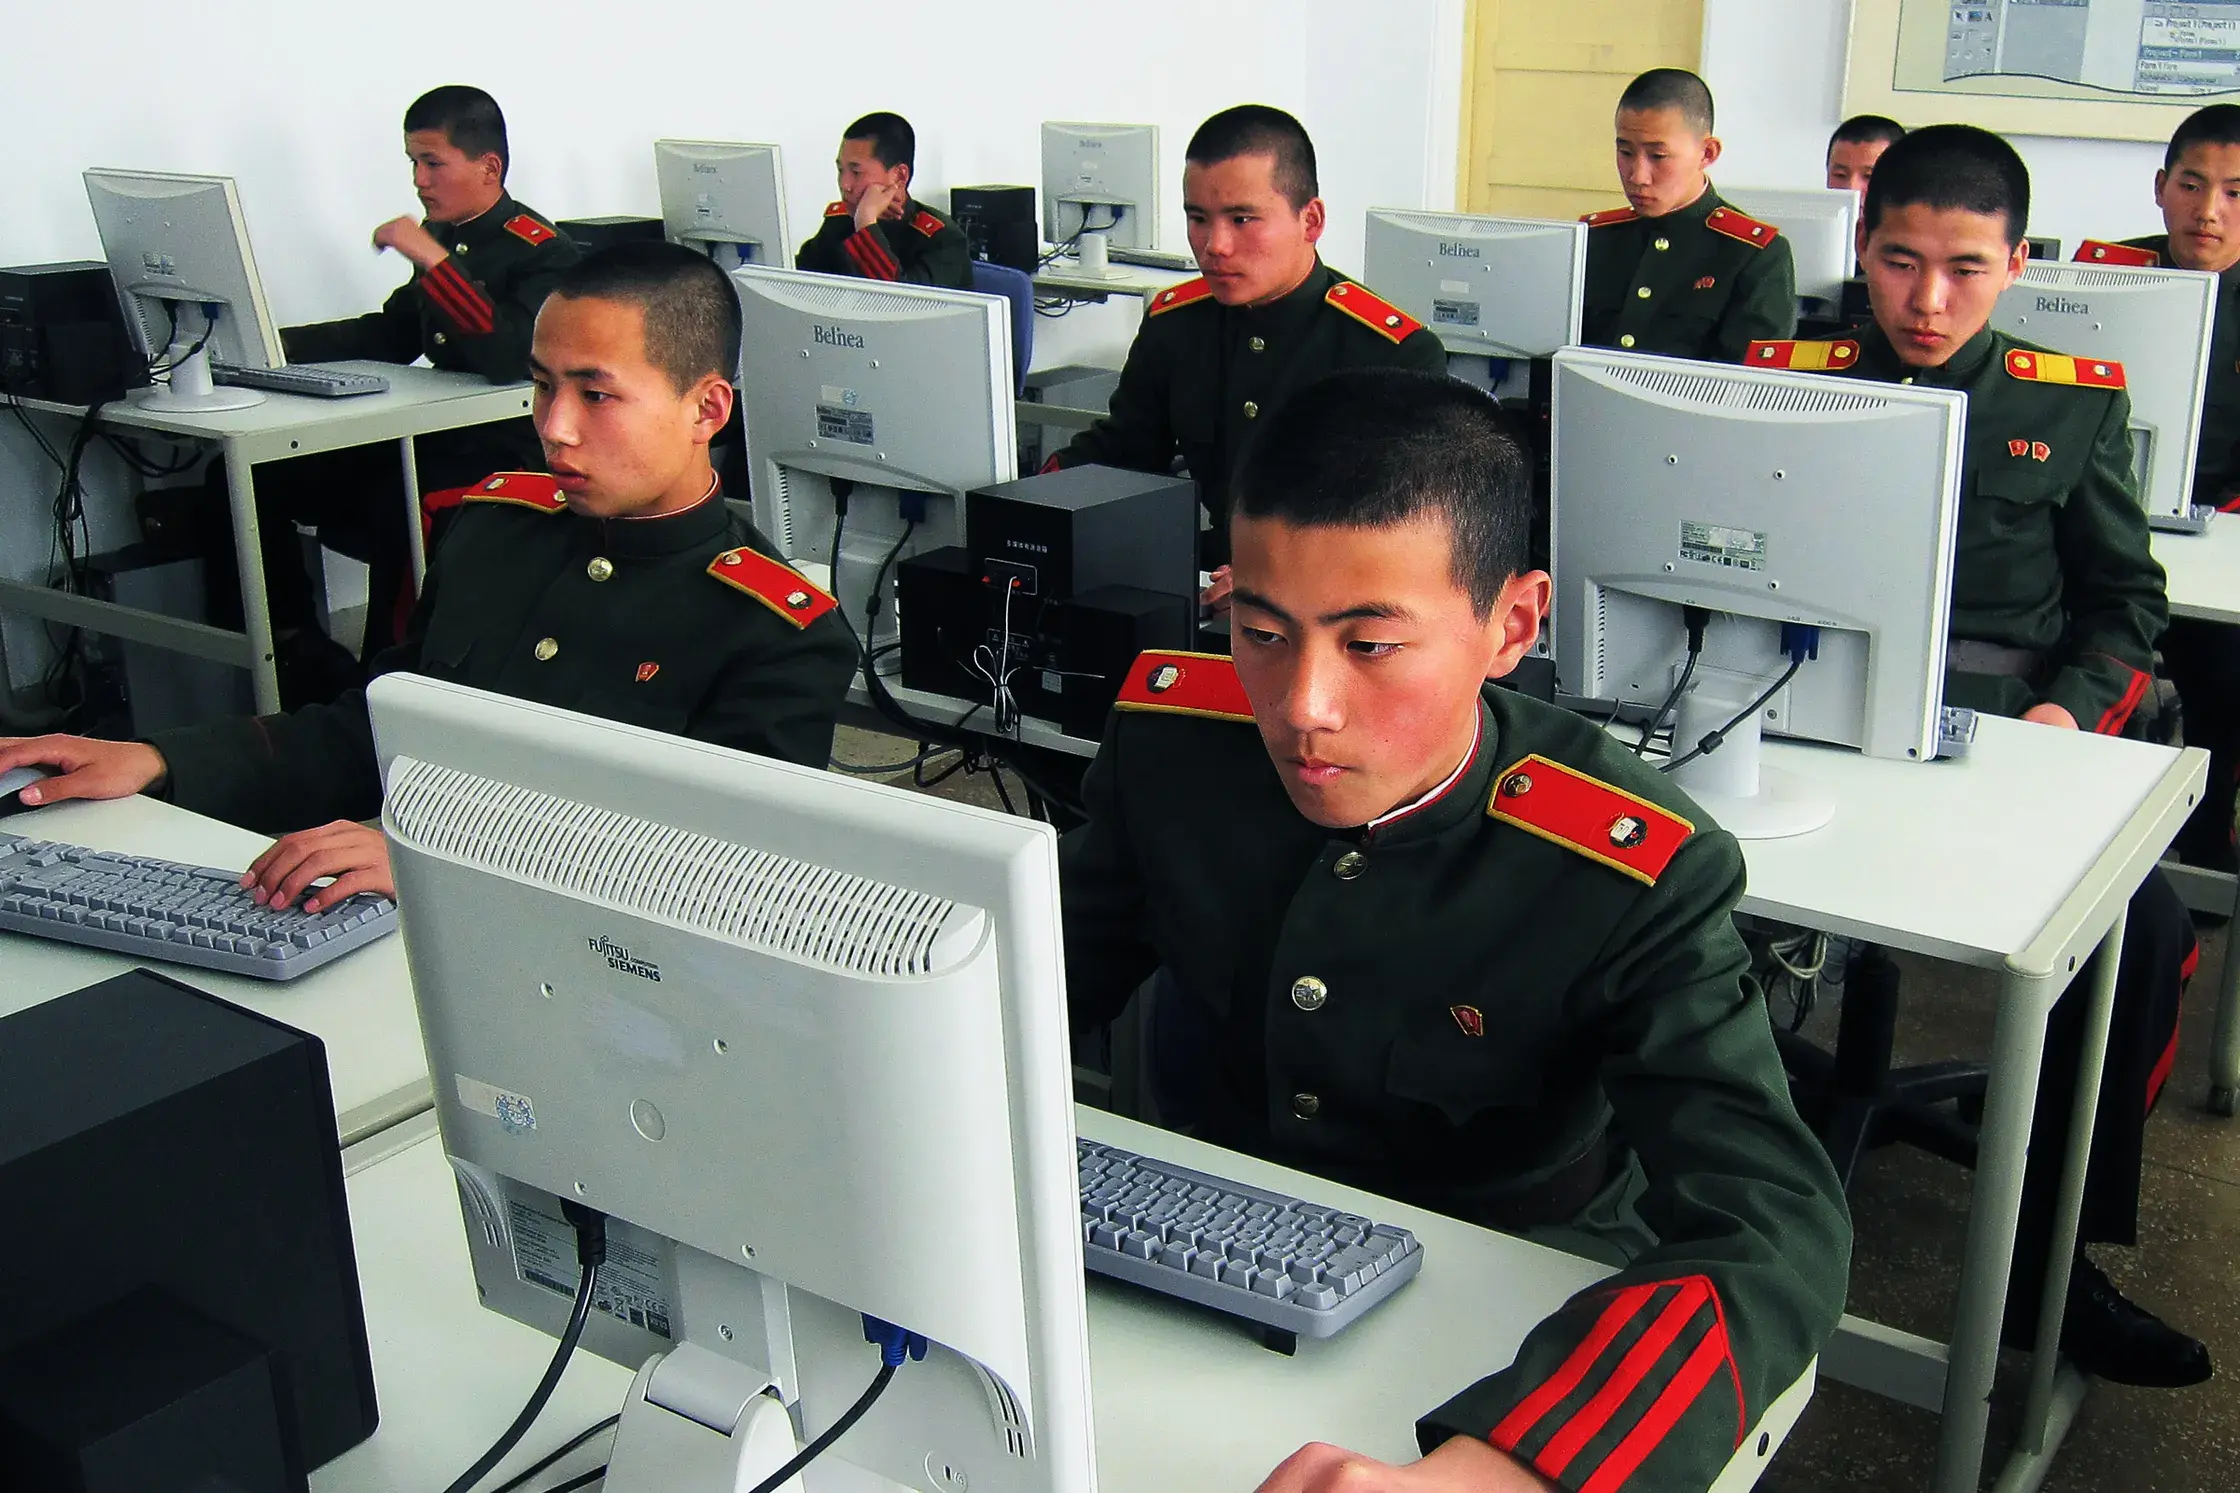
Amazon Threat Intelligence has linked recent supply chain attacks on popular NPM open-source code libraries to a North Korean hacker group.
Amazon's Threat Intelligence division has attributed a series of supply chain cyberattacks targeting open-source software libraries to a hacker group linked to North Korea. Security researchers reported that the group compromised reusable code modules hosted on the NPM package manager, a major global repository relied upon by software developers.
By injecting malicious code into widely integrated open-source packages, the perpetrators sought to infiltrate downstream corporate networks and development environments. Amazon emphasized that supply chain compromises remain a favored strategy for state-sponsored operators aiming to covertly gain access to targeted organizations through trusted software dependencies.
Sources: The Insider.