
Russia, Iran or Opportunistic Hackers? Who is Behind Europe’s Supermarket Cyberattacks

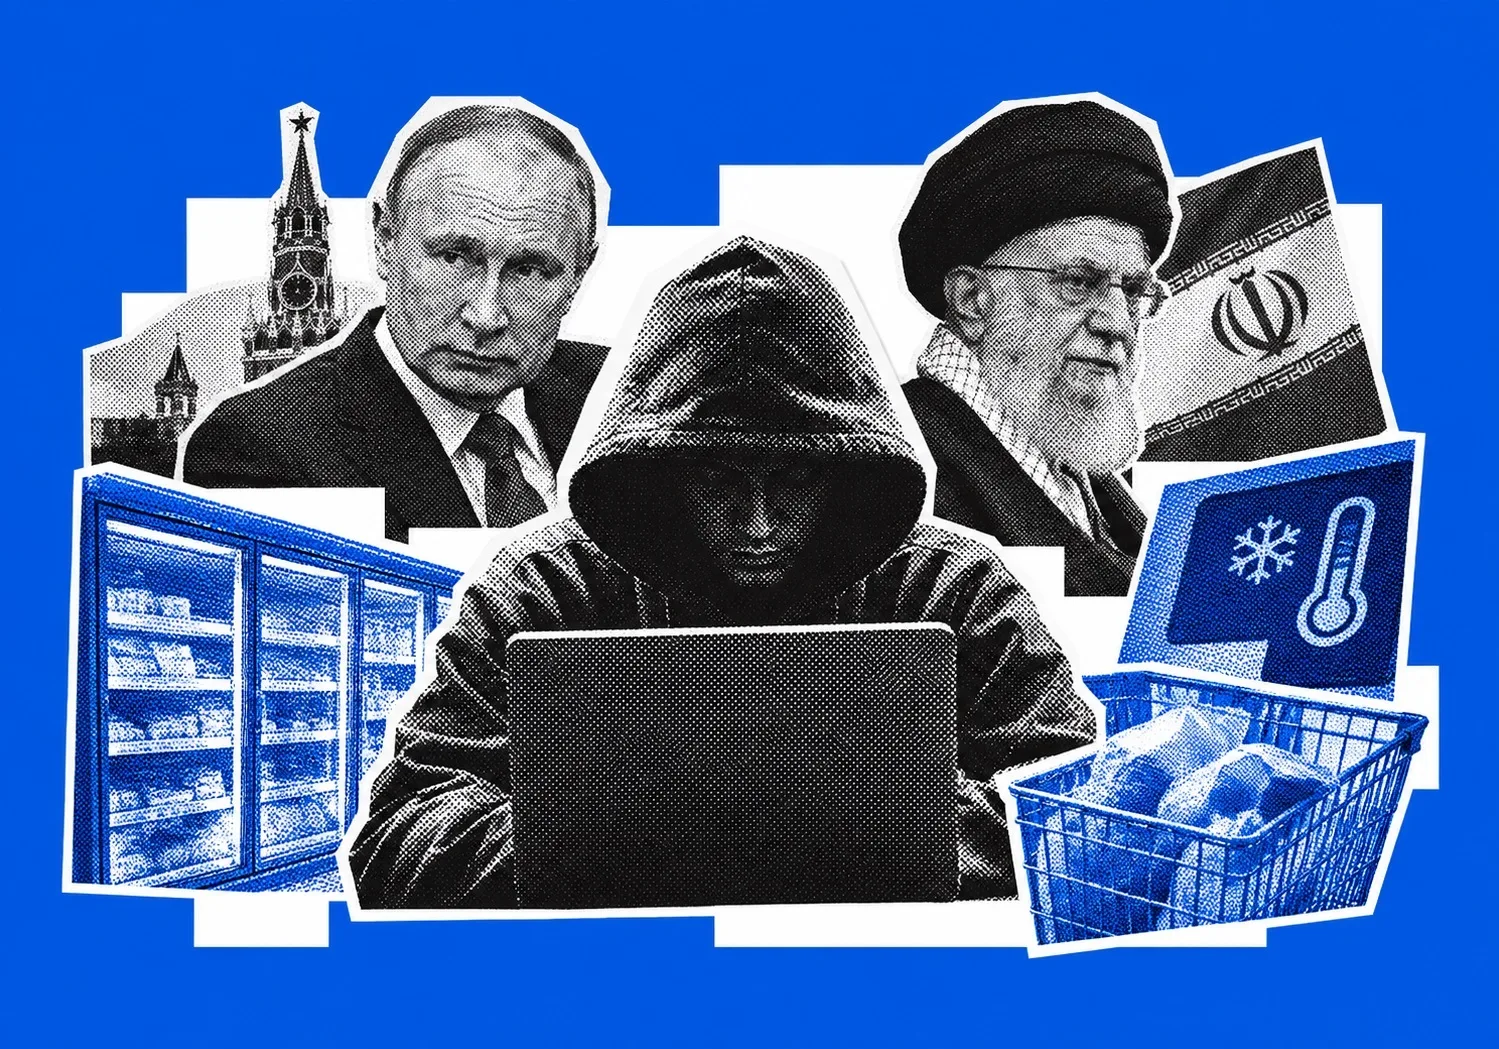
Conflicting claims by pro-Russian hacktivist groups NoName057(16) and Z-Pentest Alliance have deepened the mystery surrounding the cyberattacks on European supermarket refrigeration systems. As investigators examine potential Russian, Iranian, or independent hacker involvement, the November incidents highlight a growing threat to Europe's physical critical infrastructure.
According to BBC reporting, NoName057(16) and Z-Pentest Alliance published messages celebrating the attacks before the posts and channels became unavailable. The groups claimed to have demonstrated their technical capabilities, but investigators have not established whether either organisation actually carried out the intrusions.
The uncertainty matters because the attacks did more than temporarily disable digital services. They interfered with equipment used to preserve food, causing financial losses and forcing retailers to withdraw products from sale.
As Nexus Europa previously reported, the November incidents followed a larger wave of refrigeration-system attacks in France in October. The earlier operation affected approximately 700 premises and resulted in losses estimated in the millions of euros.
The latest developments shift attention away from how the equipment was compromised and towards a more difficult question: whether the attacks form part of a broader campaign against European infrastructure or reflect the activities of loosely connected hackers exploiting accessible systems.
Pro-Russian hackers claim responsibility, then disappear
NoName057(16) and Z-Pentest Alliance are established names in the pro-Russian hacktivist environment. Both have histories of targeting organisations in countries supporting Ukraine, although their operational methods differ.
Their reported claims concerning the supermarket incidents appeared after refrigeration systems had been disrupted in multiple European countries.
The subsequent disappearance of the messages and Telegram channels raises questions about the reliability of those claims. However, the removal of online material does not establish that the statements were false. Nor does it demonstrate that the groups were responsible.
The distinction is particularly important in the world of politically motivated hacking, where public claims can serve purposes beyond reporting an actual intrusion.
Hacktivist organisations may use successful attacks to attract supporters, demonstrate their capabilities or amplify political messages. They can also exaggerate the scale of relatively limited operations.
A December 2025 joint cybersecurity advisory, issued by US agencies and international partners, specifically warned that pro-Russian hacktivists frequently make false or exaggerated claims about attacks on critical infrastructure.
The advisory identified NoName057(16), Z-Pentest and the Cyber Army of Russia Reborn among the groups conducting opportunistic operations against industrial control systems.
It also noted that attackers sometimes misidentify the organisations whose systems they have accessed.
This makes a Telegram statement a potentially useful investigative lead, but not independent proof of responsibility.
What investigators know about the possible perpetrators
The investigation has not produced a publicly confirmed attribution of the supermarket attacks.
According to the BBC, cybersecurity researchers examining the incidents have identified several competing possibilities.
French cybersecurity company Sequoia reportedly found that aspects of the attacks were consistent with techniques associated with Russia-linked hackers. However, the company also raised the possibility of Iranian involvement, citing similarities with previous operations targeting supermarkets in Israel.
Other cybersecurity firms investigating the incidents reportedly considered a less politically significant explanation: an individual, potentially a teenager, exploiting accessible equipment for amusement or notoriety.
These possibilities are not equally substantiated, and none should be treated as an established explanation.
The similarities between incidents may help investigators identify shared methods, but they do not necessarily reveal who directed an operation.
Different groups can exploit the same vulnerabilities, use similar publicly available tools and imitate one another's techniques.
The problem becomes particularly acute when attacks involve poorly protected industrial equipment rather than sophisticated malware developed for a specific target.
In such circumstances, investigators need more than evidence of how an intrusion occurred. Establishing responsibility may require reliable technical records, evidence connecting the activity to known operators and corroboration from other investigative sources.
For European authorities, the distinction between a politically directed operation and an opportunistic intrusion is significant. Both can cause economic damage, but they raise different questions about international responsibility and the appropriate response.
The Russian connection: What is already established?
Although responsibility for the supermarket incidents remains uncertain, the activities and organisational backgrounds of the two groups are considerably better documented.
According to the multinational cybersecurity advisory published in December 2025, NoName057(16) emerged in 2022 and became known primarily for distributed denial-of-service attacks against government institutions and private organisations in NATO member states and other European countries.
Such attacks typically overwhelm online services with traffic, making websites or digital platforms temporarily inaccessible.
The advisory assessed that Russia's Center for the Study and Network Monitoring of the Youth Environment, known as CISM, created NoName057(16) as a covert project.
According to the participating security agencies, CISM personnel developed and customised the group's DDoSia attack tool, financed its network infrastructure, administered Telegram channels and selected targets.
Z-Pentest followed a different trajectory.
Established in September 2024, it brought together members of NoName057(16) and the Cyber Army of Russia Reborn, commonly known as CARR.
The advisory assessed that CARR's formation had probably been supported by a Russian military intelligence unit. It also described disagreements over the level of support and funding received from Russian intelligence as a factor behind the creation of Z-Pentest.
Unlike NoName057(16), Z-Pentest has concentrated on operational technology intrusions, including attempts to manipulate equipment used by industrial and infrastructure operators.
Its activities have involved accessing control interfaces and publicising alleged intrusions through images and videos.
These documented relationships demonstrate why investigators would examine the possibility of Russian involvement in attacks on European refrigeration equipment.
They do not, however, establish that Russian intelligence directed the November supermarket incidents or that either group conducted them.
Why the EU sanctioned Z-Pentest before the supermarket attacks
The European Union had already taken action against Z-Pentest months before the latest incidents.
On 13 July 2026, the Council of the European Union announced sanctions against nine individuals and four entities associated with Russian cyber operations and destabilising activities.
Z-Pentest was among the sanctioned organisations.
The Council described it as a pro-Russian hacktivist group targeting critical infrastructure internationally, particularly the energy and water sectors.
It specifically attributed a December 2024 cyberattack against a Danish water utility to Z-Pentest.
The sanctions also targeted Yuliya Pankratova, identified as the group's leader, and Denis Degtyarenko, described as a principal hacker. Both were associated with CARR.
The Council stated that CARR was linked to Russia's military intelligence service, the GRU, and had conducted cyber campaigns against organisations in Ukraine, EU member states and other countries.
The measures include asset freezes and restrictions on making funds or economic resources available to designated individuals and entities.
For European policymakers, the significance of these sanctions extends beyond the individual organisations.
They reflect an established concern that loosely organised, politically motivated hacking groups can participate in operations affecting essential infrastructure, sometimes with varying degrees of connection to state institutions.
The distinction between a state-directed operation and a sympathetic group acting independently can nevertheless remain difficult to establish in individual cases.
That uncertainty is central to the investigation into the supermarket incidents.
From website disruption to physical infrastructure damage
The wider significance of the supermarket incidents becomes clearer when placed alongside earlier attacks on industrial systems.
An October Bloomberg investigation examined cyber operations associated with Russia-linked groups that had moved beyond website disruption towards interference with physical equipment.
The cases described included attacks involving a Danish water utility, industrial facilities in Spain and infrastructure operators in the United States.
Such incidents demonstrate a change in the potential consequences of relatively accessible cyberattack methods.
A denial-of-service attack may temporarily prevent customers from accessing a website. An intrusion into an industrial control system can instead change the operation of equipment that manages water, electricity, food storage or manufacturing processes.
The technical sophistication required is not necessarily high.
The December 2025 multinational advisory warned that pro-Russian hacktivist groups frequently exploit inadequately protected remote-access connections to industrial equipment.
It described attackers using relatively basic methods to gain access to control interfaces and manipulate operating parameters.
The agencies also warned that these groups often lack detailed knowledge of the industrial processes they interfere with.
That limitation does not necessarily reduce the danger. Attackers who misunderstand the equipment they control may cause unintended damage or disruptions beyond their original objectives.
The advisory documented physical damage resulting from some operations, although it did not report injuries associated with the activities covered.
For Europe's security authorities, this creates a threat that cannot be assessed solely by examining the technical capabilities or political importance of a particular hacking group.
Even an inexperienced attacker may be able to interfere with equipment if its remote-access systems are insufficiently protected.
Why uncertain attribution complicates Europe's response
The supermarket incidents illustrate two separate problems that European authorities must address simultaneously.
The first is operational: protecting interconnected equipment against unauthorised access.
The second is political and investigative: determining who is responsible when an intrusion occurs.
The operational problem can be addressed without knowing the attacker's identity. Organisations can restrict remote connections, update vulnerable equipment and improve monitoring.
Attribution is more complicated.
If an intrusion is linked to an individual acting independently, the response may primarily involve criminal investigation and prosecution.
If it is connected to an organised group operating across borders, international law-enforcement cooperation becomes more important.
Where credible evidence establishes state involvement, governments may also consider diplomatic measures, sanctions or other responses under existing legal frameworks.
The European Union already possesses a mechanism for responding to malicious cyber activity through its cyber diplomacy toolbox and sanctions regime.
However, applying measures against particular individuals or organisations requires a defensible basis for identifying those responsible.
The July sanctions against Z-Pentest demonstrate that European institutions can take action against groups linked to hostile cyber operations. They do not mean that subsequent attacks involving similar methods can automatically be attributed to the same actors.
There is also a risk in treating every intrusion involving vulnerable industrial equipment as evidence of a coordinated geopolitical campaign.
The multinational advisory describes opportunistic targeting as a characteristic of several pro-Russian hacktivist groups. Attackers may select systems because they are accessible, rather than because the organisation operating them has particular strategic importance.
That distinction matters when evaluating attacks against supermarkets spread across different European countries.
A pattern of similar intrusions may indicate shared tools, common vulnerabilities or cooperation between attackers. It does not necessarily establish central coordination.
Europe's emerging cyber-physical security dilemma
The latest attacks have exposed a security problem extending beyond supermarkets.
Commercial and industrial equipment increasingly relies on networked control systems, while some installations remain accessible through inadequately protected remote connections.
That creates opportunities for attackers whose technical abilities may be limited but whose actions can have immediate physical consequences.
At the same time, politically motivated hacking groups operate in an environment where claiming responsibility can generate publicity regardless of whether the claim is substantiated.
The reported disappearance of NoName057(16) and Z-Pentest Alliance's Telegram statements adds another complication to the investigation, but it does not resolve the question of responsibility.
Investigators still face competing explanations involving Russia-linked groups, possible Iranian actors and opportunistic individuals.
The evidence needed to distinguish between those scenarios is separate from the evidence establishing that refrigeration equipment was compromised.
For European governments, the immediate challenge is therefore not simply identifying which geopolitical adversary may have benefited from the disruption.
It is developing the capacity to investigate attacks accurately while protecting the physical systems on which businesses and essential services increasingly depend.
The perpetrators of the November supermarket attacks remain unidentified. The vulnerabilities that made the disruption possible, however, are already part of a documented international security problem.
Sources: BBC, Australian Cyber Security Centre, Council of the EU, Bloomberg