
Estonia Links Milrem Robotics Arson to Russian Intelligence

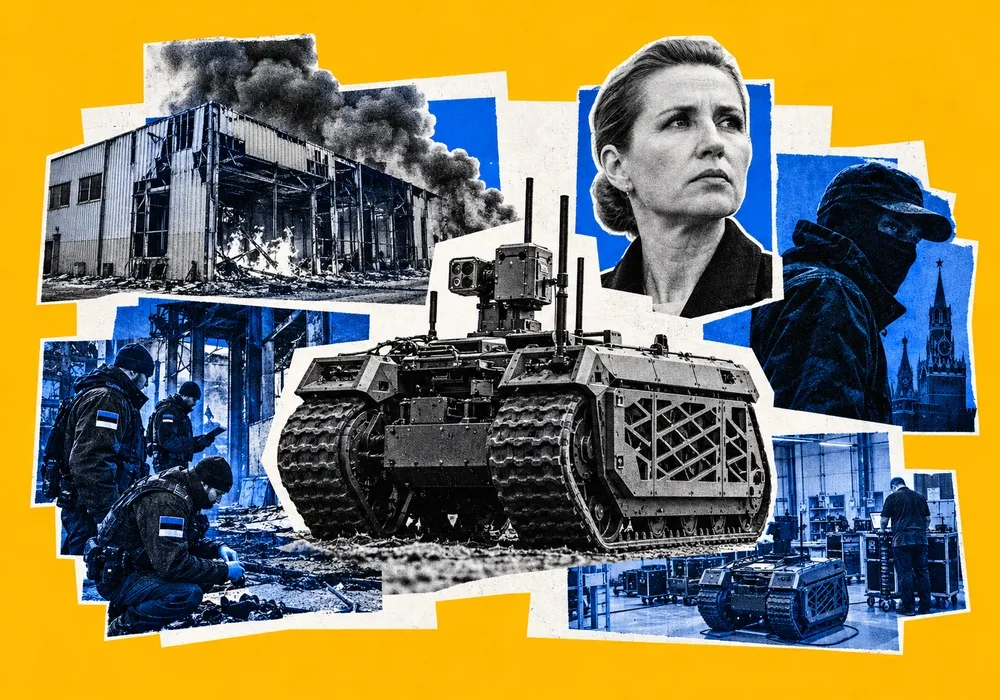
Estonia has concluded that Russian intelligence commissioned the August arson attack on Milrem Robotics, a defence technology company supplying unmanned ground systems to Ukraine. The case highlights the growing security risks facing Europe's expanding defence industry, as sabotage operations increasingly cross national borders and rely on local recruits.
Estonia has concluded that an arson attack on a building used by defence technology company Milrem Robotics in Tallinn was commissioned by Russian intelligence services, turning an initially investigated case of property destruction into a broader European security issue. The company develops unmanned ground systems and supplies its technology to Ukraine, making the incident particularly significant as European governments seek to expand defence production and deepen industrial cooperation with Kyiv.
The fire broke out overnight on August 15 at a building used by Milrem Robotics on Betooni Street in Tallinn's Lasnamäe district. Emergency services brought the fire under control and no one was injured. At the time, Estonian authorities treated the incident as a possible case of arson and opened a criminal investigation, while investigators examined whether it could have been an act of sabotage.
The investigation quickly developed a cross-border dimension. Latvia's State Security Service detained two Latvian citizens on August 17 and a third suspect the following day. Investigators searched seven locations connected with the suspects and seized numerous data-storage devices as well as objects that could have been used to start the fire. Latvia's security service said the case was being investigated in close cooperation with its Estonian counterparts.
The three suspects were subsequently transferred to Estonia in September and placed in custody there. Estonian prosecutors had initially said that they were examining several possible motives, including whether the attack constituted sabotage, while evidence was still being collected.
That assessment changed on September 29. Estonia's Internal Security Service, KAPO, concluded that the attack was a deliberate and pre-planned act commissioned by Russian special services. Prime Minister Kristen Michal said the conclusion was based on security information collected and assessed by KAPO.
The Estonian government has presented the attack as part of a wider Russian campaign in Europe. Foreign Minister Margus Tsahkna said Russia's chargé d'affaires would be summoned in Tallinn over the incident. The Kremlin rejected the accusations, with spokesperson Dmitry Peskov describing them as unfounded and saying that Estonia had not provided evidence publicly.
Why Milrem was a significant target
Milrem Robotics is not a conventional defence contractor. The Estonian company specialises in unmanned and autonomous ground systems, placing it within one of the fastest-developing areas of European military technology.
Its THeMIS unmanned ground vehicle has been supplied to Ukraine, where unmanned systems are used for tasks including logistics, reconnaissance and explosive ordnance disposal. The war has accelerated the development of such technologies, as militaries seek ways to perform dangerous tasks without exposing personnel to the same level of risk.
The company therefore occupies an increasingly important position between European defence production and Ukraine's battlefield requirements. Its activities also reflect a broader shift in European defence policy towards autonomous systems, robotics and technologies that can be developed and tested through cooperation with Ukraine.
An attack on such a company has implications beyond the immediate physical damage. Even when production or deliveries are not interrupted, the incident can create additional security costs, require companies to strengthen physical protection and potentially discourage smaller defence-technology firms from expanding operations.
In this sense, the Milrem case illustrates a vulnerability created by Europe's effort to rapidly rebuild and expand its defence-industrial base. The more companies become involved in supplying Ukraine and integrating Ukrainian battlefield experience into European defence development, the more their facilities form part of the wider security environment.
A cross-border operation
The involvement of Latvian suspects is also important. The people accused of carrying out the attack were not Estonian citizens, and the investigation required cooperation between security services and prosecutors in two neighbouring EU and NATO member states.
Latvia's State Security Service said the suspects were investigated for both arson and providing assistance to a foreign state in an action directed against another state. The service's investigation included searches of residences and vehicles and the seizure of digital evidence.
The case demonstrates how sabotage operations can exploit the movement of people across Europe's internal borders. An operation can be planned in one country, carried out in another and involve recruits or intermediaries from elsewhere.
That creates a particular challenge for European security agencies. Traditional national approaches to physical security are less effective when the people carrying out an attack can cross borders with relative ease, while the intelligence behind an operation may originate outside the European Union altogether.
For the Baltic states, this issue has an additional dimension. Estonia, Latvia and Lithuania are all members of both NATO and the EU and are among Europe's most active supporters of Ukraine. Their geographic position also puts them directly on NATO's eastern flank, close to Russia and Belarus.
The recruitment problem
Estonian security officials have warned that Russian intelligence services can rely on intermediaries rather than professional operatives. According to KAPO's assessment, recruitment efforts can target people motivated primarily by money and who may not fully understand who is ultimately behind an assignment.
The significance of that model is that it lowers the operational cost of sabotage. A foreign intelligence service does not necessarily need to send its own personnel into a European country to damage a facility. It can instead identify people willing to carry out relatively simple tasks in exchange for payment.
That makes the threat harder to detect before an incident occurs. A person approached online may have no previous connection to intelligence work and may initially understand the assignment as ordinary criminal activity.
Estonian security officials said that Russian services have attempted to recruit people from different backgrounds, including people in the Russian-speaking community, individuals connected to organised crime and foreign nationals. KAPO's director-general Margo Palloson said Russian services continued to search for people willing to carry out attacks, while many planned operations had been prevented before they could be executed.
The Milrem investigation therefore offers European security services another example of how foreign intelligence activity can be outsourced to local or regional actors.
Defence companies face a changing security environment
The incident comes as European countries are spending more on defence and trying to expand industrial capacity after years in which production levels were insufficient for the requirements exposed by the war in Ukraine.
This expansion involves not only major weapons manufacturers. Smaller companies working on drones, robotics, sensors, software, ammunition components and other specialised technologies are becoming increasingly important to European defence planning.
Many of these companies are also deeply integrated into cross-border supply chains. A technology company based in Estonia may cooperate with manufacturers in Poland, the Netherlands or other European countries while supplying equipment to Ukraine.
That interconnected structure creates opportunities for industrial cooperation, but it also means that an attack on one company can potentially have consequences beyond its own premises.
The security challenge is therefore becoming broader than protecting military bases or critical infrastructure. Defence manufacturers, research facilities, warehouses, logistics companies and technology suppliers increasingly need to be treated as part of Europe's security architecture.
The Milrem case adds a physical dimension to this problem. European companies already face cyberattacks, espionage and attempts to obtain sensitive technical information. Physical sabotage introduces another layer of risk at precisely the moment when governments are encouraging more private companies to enter the defence sector.
Ukraine remains central to the wider picture
The connection to Ukraine is particularly important because European governments are simultaneously trying to maintain military support for Kyiv and increase their own defence capabilities.
Ukraine has become a major testing ground for technologies such as drones, unmanned ground vehicles and electronic warfare systems. European companies increasingly cooperate with Ukrainian institutions and manufacturers to adapt those technologies for battlefield use and future European requirements.
Milrem's THeMIS vehicles are part of that process. Their use in Ukraine has given the company experience with a technology category that European armed forces are themselves increasingly interested in developing.
This creates a direct overlap between support for Ukraine and the development of Europe's own defence capabilities. Disrupting a company that contributes to Ukrainian military capacity can therefore potentially affect both objectives at once.
Estonian authorities have explicitly linked the Milrem attack to what they describe as a broader Russian effort to intimidate European countries and weaken their support for Ukraine. That interpretation is Tallinn's assessment rather than an independently established conclusion about Moscow's wider strategic intentions, but it reflects how Baltic governments are increasingly approaching sabotage as part of the broader security confrontation surrounding the war.
Part of a wider European concern
The Milrem incident is not occurring in isolation. European governments have reported a growing number of cases involving suspected sabotage, arson, cyber operations and other forms of hostile activity attributed to or linked to Russian state interests since the full-scale invasion of Ukraine.
The pattern has included incidents affecting infrastructure as well as companies connected with defence production and support for Ukraine. European authorities have increasingly described these activities as hybrid operations because they fall below the threshold of conventional military attack while still seeking to impose costs on European states.
For Estonia, the geographical proximity to Russia makes the issue particularly acute. But the model is relevant across Europe because the same recruitment and proxy mechanisms can operate across national borders.
The fact that the suspects in the Milrem case were Latvian citizens, detained in Latvia and later transferred to Estonia demonstrates the practical importance of European security cooperation. The investigation would have been considerably more complicated without the ability of the two countries' authorities to exchange information and coordinate arrests and evidence gathering.
Security costs of Europe's defence expansion
The case also raises a longer-term question for European defence policy: how much additional security infrastructure will be required as the defence industry expands?
Governments are encouraging companies to increase production, build new facilities and establish international partnerships. But a larger industrial base also creates a larger potential target set.
For major manufacturers, extensive security infrastructure may already be part of normal operations. Smaller technology companies can face a different situation. Their facilities may resemble ordinary industrial or commercial premises, even though the technologies developed or assembled inside them have direct military applications.
That gap can make physical security a particular concern for smaller defence firms. Strengthening access controls, surveillance, cyber protection and employee security can add significant costs at a time when governments are already trying to accelerate production.
The Milrem case could therefore reinforce calls for closer cooperation between national security services and private defence companies. It also demonstrates the importance of companies reporting suspicious approaches or activity before an incident takes place.
Estonia's response
Tallinn has signalled that the attack will not lead it to reduce support for Ukraine. Instead, Estonian officials have said the country will continue working with European partners to strengthen pressure on Russia and improve its own security preparedness.
The government has also stressed that similar Russian-linked operations have been disrupted before they could be carried out. KAPO's director-general said most of the Russian-planned attacks identified in Estonia had been prevented, although he did not disclose operational details.
That distinction is important. The Milrem attack was limited in its immediate physical impact: the fire was contained quickly, nobody was injured and the company said the incident did not stop its wider operations. But the fact that the perpetrators were able to reach a defence-related facility remains significant from a counter-intelligence perspective.
For European governments, the objective is increasingly not simply to respond after an attack but to identify recruitment networks and planned operations before they reach the execution stage.
The Milrem case will remain subject to a criminal investigation, and the full evidentiary basis for Estonia's attribution has not been made public. Nevertheless, the government's conclusion marks a clear escalation in the official treatment of the incident.
What began as a fire at an industrial building in Tallinn has become another example of the security pressures facing Europe's defence sector. As European countries expand production, deepen cooperation with Ukraine and invest in new military technologies, protecting the companies behind those efforts is becoming an increasingly important part of the continent's defence policy.