
Iran’s Covert Operations Put European Security on Alert
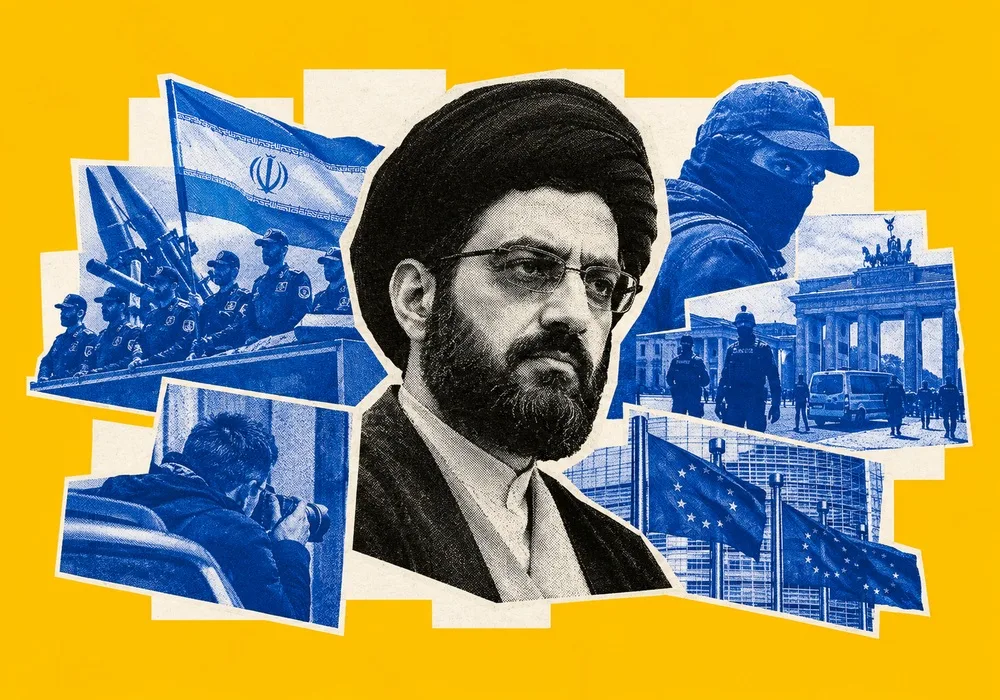
European intelligence services are warning that Iranian-linked espionage, sabotage and cyber operations are becoming a persistent security challenge. The growing use of criminal intermediaries and individuals recruited online is complicating efforts to attribute attacks, protect potential targets and coordinate Europe’s response.
European intelligence services are increasingly concerned that Iran’s confrontation with Western powers is extending beyond the Middle East into a sustained campaign of covert operations across Europe. Alleged assassination plots, arson attacks, surveillance of military installations and cyber espionage have prompted governments to reassess the scale of the threat and the effectiveness of existing counter-intelligence measures. Although some investigations have yet to establish direct links to the Iranian state in court, security officials argue that the pattern of incidents points to a persistent challenge that extends beyond individual attacks.
On 12 October, 32 countries, including the United Kingdom, France, Germany, the United States, Canada and the Netherlands, jointly condemned Iranian-linked violent operations, sabotage, cyberattacks and other hostile activities. The statement reflected growing concern that Tehran could use indirect methods to retaliate against Western governments following the military confrontation involving Iran, the United States and Israel. Such operations allow a state to exert pressure without resorting to conventional military action, while the involvement of intermediaries can make attribution and retaliation more difficult.
The United Kingdom has emerged as a particularly prominent focus of these concerns. On 27 October, British authorities brought charges against two men in connection with a national security investigation involving RAF Fairford, a military base that had hosted American aircraft involved in operations against Iran. The investigation followed an incident on 27 September, when suspicious activity near the installation raised concerns about a possible attempt to target military aircraft. British authorities have linked the case to suspected Iranian intelligence activity, although the allegations remain subject to legal proceedings. The case illustrates how military infrastructure used by allied forces can become a potential target even when a country is not directly engaged in combat on its own territory.
The British security service MI5 has reported more than 50 arrests since the beginning of 2026 in connection with hostile Iranian-linked activity. The suspected targets extend beyond Iranian dissidents in exile and opposition media to Jewish communities, Israeli interests and military installations. London has also imposed sanctions on individuals alleged to have been involved in operations linked to Iranian security structures and criminal networks. Tehran has rejected British accusations, maintaining that they are politically motivated and intended to deflect responsibility for the conflict.
Criminal networks as instruments of state pressure
One of the most significant challenges for European counter-intelligence agencies is the reported use of individuals without established links to intelligence services. Recruitment through online platforms, financial incentives and criminal intermediaries can provide foreign intelligence organisations with a degree of operational distance from the people carrying out surveillance or attacks. Individuals recruited in this way may be tasked with collecting information, identifying security weaknesses or targeting particular locations, without necessarily understanding the wider operation in which they are participating.
This approach complicates conventional counter-terrorism investigations. Authorities must distinguish between independently motivated criminal activity, attacks claimed by proxy organisations and operations that may have been commissioned or directed by a foreign state. Establishing the relationship between an individual suspect and a foreign intelligence service requires evidence that can withstand judicial scrutiny. Consequently, intelligence assessments may identify a suspected state connection before prosecutors are able to demonstrate it in court.
Cases in Germany and the United Kingdom illustrate the range of alleged activities. On 14 October, a court in Hamburg sentenced two men in connection with a plot targeting Jewish public figures and businesses, with the principal defendant found to have acted under the control of Iran’s Quds Force, the external operations branch of the Islamic Revolutionary Guard Corps. Other investigations have concerned alleged surveillance of Israeli diplomatic facilities, Jewish institutions and opposition media. In several European countries, attacks against Jewish and Israeli-linked sites have also been claimed by Harakat Ashab al-Yamin al-Islamia, a group associated with pro-Iranian militant networks.
The implications extend beyond the immediate physical damage caused by such incidents. Surveillance of military facilities can reveal operational routines and security vulnerabilities, while attacks on Jewish institutions and opposition media can intimidate communities and undermine the ability of dissidents to organise freely. Even unsuccessful plots can impose additional costs on public authorities by requiring more intensive protection for sensitive sites, diplomatic facilities and individuals considered potential targets.
Cyber operations widen the threat
The suspected Iranian campaign also has a digital dimension. In September, the United Kingdom and its partners disclosed information about a spyware tool known as Chosen Brick, which they attributed to Iranian state-linked actors. The tool was reportedly used to target dissidents, activists and journalists opposed to Tehran. Investigators said the operation could involve impersonating trusted contacts on messaging platforms such as WhatsApp and Telegram to obtain sensitive information.
Such techniques exploit a vulnerability that cannot be addressed solely through physical security or conventional intelligence gathering. Diplomatic personnel, journalists, researchers and members of diaspora communities increasingly depend on digital communications that may expose their contacts, movements and professional relationships. Compromised accounts can also be used to approach additional targets, making a single successful intrusion a potential starting point for a broader intelligence operation.
For European governments, this creates a need to treat physical and digital security as interconnected responsibilities. Information obtained through cyber espionage could help identify individuals for surveillance or intimidation, while details gathered on the ground could support subsequent digital targeting. Protecting vulnerable communities therefore requires cooperation between intelligence services, law enforcement agencies and organisations responsible for cybersecurity, alongside practical guidance for those at risk.
A test of European coordination
The perceived increase in Iranian-linked activity raises a wider question about Europe’s ability to respond consistently to threats that cross national borders. Intelligence may be collected in one country, a suspect recruited in another and a potential target located elsewhere. Criminal networks can operate across several jurisdictions, while the evidence needed for prosecution may be distributed between national authorities. Effective responses consequently depend on timely intelligence-sharing, coordinated investigations and common assessments of the risks facing European infrastructure and communities.
The threat is not assessed equally across the continent. French officials have acknowledged an increase in Iranian-linked activity but have indicated that the situation differs from that in the United Kingdom and Germany, where authorities identify a wider range of potential targets. National differences in exposure, intelligence capabilities and the concentration of vulnerable communities mean that a single European response will need to accommodate different levels of risk.
At the same time, the growing number of reported incidents places pressure on governments to balance preventive action with legal safeguards. Intelligence agencies may need to act on incomplete information to prevent an attack, while criminal proceedings require evidence capable of establishing individual responsibility. Excessive reliance on unverified attribution risks undermining public confidence, but fragmented investigations and delayed information-sharing could leave opportunities for hostile networks to exploit gaps between national systems.
The central challenge for Europe is therefore not simply to prevent individual attacks, but to make covert operations more difficult to organise, conceal and repeat. That requires stronger protection for military sites and vulnerable communities, better coordination against transnational criminal intermediaries, and greater resilience against digital espionage. If the current pattern persists, countering foreign interference will become an increasingly important part of European security policy, even in the absence of direct military confrontation on European territory.
Sources: Le Monde, The Guardian